Servers - MFT Server
The MFT Settings window, opened from Servers -> Managed File Transfer, is where the MFT Server is turned on and where its servers, endpoints and users are managed.
The MFT Server hosts file transfer servers inside the VisualCron Server. Three server types can be created:
- "SFTP": SSH File Transfer Protocol, with a fixed set of SSH algorithms
- "SFTPAdvanced": SSH File Transfer Protocol, with a selectable list of SSH algorithms
- "FTP": FTP, either unencrypted or FTPS (FTP over TLS or SSL)
Each server listens on one or more endpoints. An endpoint is an IP address and a port.
Hosting the servers in VisualCron means no separate file transfer server has to be installed, and the MFT Server Trigger can start a Job when something happens on a server, for example when a file is received or sent, or when a folder is created.
- A new endpoint listens on all IPv4 addresses of the Server computer ("0.0.0.0").
- A new FTP endpoint uses port 21 and the security type "None", so user names, passwords and files are sent unencrypted. Select "TSL" or "SSL" and a certificate to encrypt the connection.
- A new SFTP or SFTPAdvanced endpoint uses port 22 and allows password authentication only.
- A new MFT server starts as soon as it is saved, and every server in the "Active" state starts again when the VisualCron Server starts, as long as Allow MFT is checked.
- Saving a permission can add a folder permission with every right checked; see Permission window below.
- The Firewall allows button does not change the rule for the endpoint port; see Firewall allows under Server Settings window: SFTP Endpoints tab below.
The Server type can only be changed while the MFT server is being added. When an existing MFT server is edited, the list is read-only, and only the endpoint tab that matches the type is shown.
Encryption, key exchange, MAC and public key algorithms can be selected only on the "SFTPAdvanced" server type. To control the algorithm list for an existing "SFTP" server, add a new MFT server of type "SFTPAdvanced" instead.
MFT Settings window
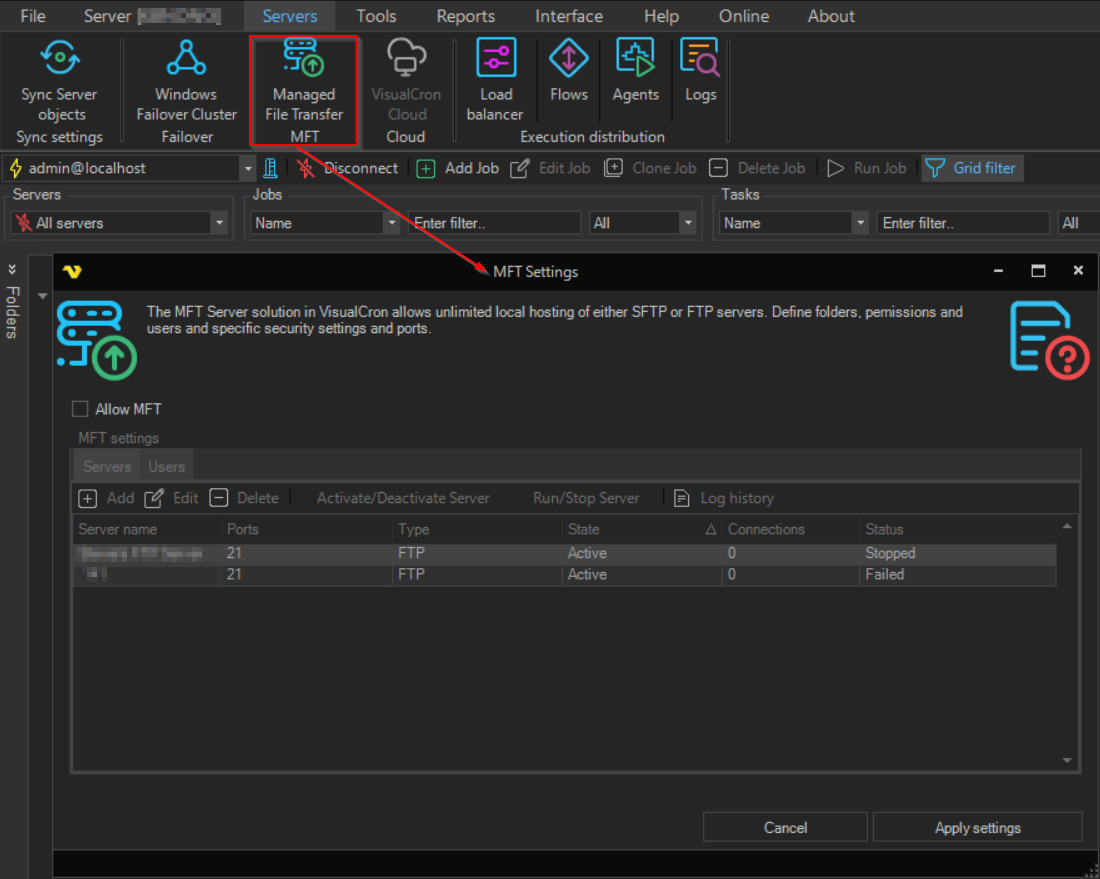
- Allow MFT: turns the MFT Server on for this VisualCron Server. While it is unchecked, the MFT settings area is unavailable. Unchecking it stops every running MFT server at once, before Apply settings is clicked, and Cancel does not start them again
- Apply settings: saves the Allow MFT setting and closes the window
- Cancel: closes the window without saving the Allow MFT setting
- Unchecking Allow MFT stops every running MFT server at once; Cancel does not start them again.
- Changes to an MFT server or user are sent to the VisualCron Server when Save is clicked in the Server Settings or User settings window. Endpoint and permission changes, including Delete, are sent only with that Save; Cancel in that window discards them.
- Delete on the Servers and Users tabs takes effect at once, without confirmation. Cancel in the MFT Settings window does not undo any of these.
The MFT settings area has two tabs: Servers lists the hosted MFT servers and Users lists the accounts that connect to them.
Servers tab
The grid shows the Server name, Ports, Type, State, Connections and Status of each MFT server. The toolbar has the following buttons:
- Add: opens the Server Settings window for a new MFT server
- Edit: opens the selected MFT server. Double-clicking a row does the same
- Delete: stops the selected MFT servers if they are running, then deletes them. No confirmation is asked. Pressing the Delete key in the grid does the same
- Activate/Deactivate Server: switches the selected servers between the "Active" and "Inactive" states. Only "Active" servers start when the VisualCron Server starts
- Run/Stop Server: stops a running server, or starts a stopped or failed one
- Log history: opens the transfer log
Right-click a server for Log history, for Export ..., which exports the server definition, and for Send to connection ..., which copies the server, its permissions and their users to another VisualCron Server.
The Users tab is described in MFT Settings window: Users tab below.
Server Settings window
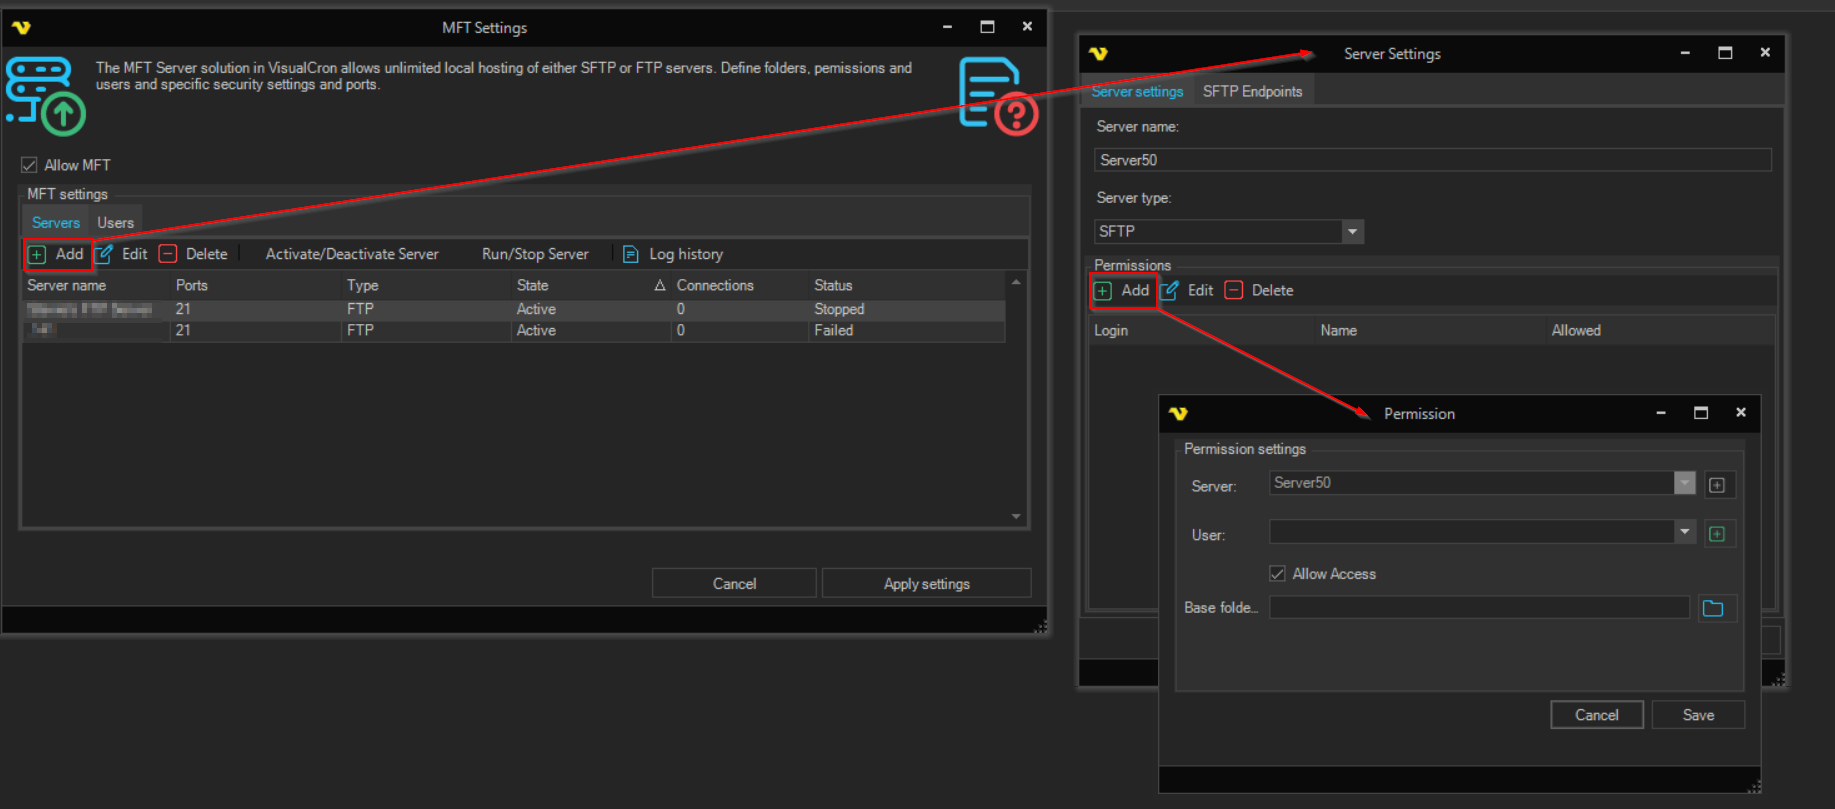
Server settings tab
- Server name: the name of the MFT server
- Server type: "FTP", "SFTP" or "SFTPAdvanced". The type decides which endpoint tab is shown next to Server settings: FTP Endpoints, SFTP Endpoints or Advanced SFTP Endpoints
- Permissions: the users who can connect to this MFT server. Use Add, Edit and Delete on the toolbar
At least one endpoint must be added before the server can be saved. A server can be saved without permissions, but no user can connect to it until one is added.
Permission window
- Server: the MFT server the permission applies to. Click the add icon next to the list to create a new MFT server
- User: the MFT user the permission applies to. Click the add icon next to the list to create a new MFT user. Both a server and a user must be selected before the permission can be saved
- Allow Access: checked by default. When checked, the user can connect to the server. Uncheck it to deny access without removing the permission
- Base folder: the startup folder for the user on this server. Use the folder button to select a folder
When the permission is saved and the user has no folder permission for this server and Base folder, one is added with every right checked, including File Delete, Folder Delete and Folder + Subfolders. Review it on the Permissions tab of the User settings window.
Server Settings window: SFTP Endpoints tab
This tab is shown for MFT servers of type "SFTP".
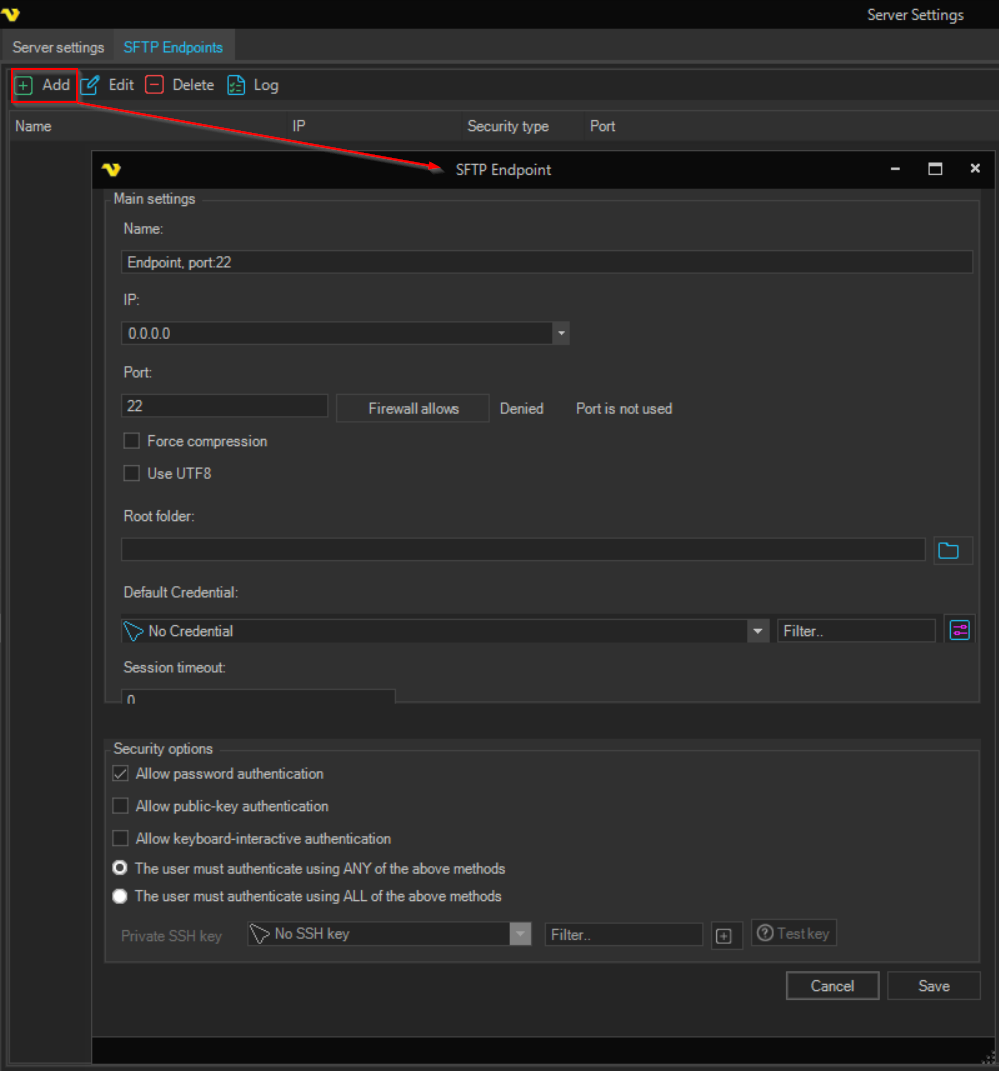
The grid shows the Name, IP, Security type and Port of each endpoint. The toolbar has Add, Edit, Delete and Log. Add and Edit open the SFTP Endpoint window.
Main settings
- Name: a name for the endpoint. A name is required. A new endpoint is named after its port
- IP: the address the endpoint listens on. "0.0.0.0", the default, means all IPv4 addresses of the Server computer. The list also offers the IPv4 addresses of the computer the Client runs on
- Port: the port the endpoint listens on. The default is "22". Next to the port, the window shows whether a VisualCron firewall rule exists for the port ("Allowed" or "Denied") and whether another process already uses the port
- Firewall allows: adds or removes a Windows Firewall rule created by VisualCron. The status next to it is checked for the endpoint port, but the rule the button adds or removes is for the VisualCron Server port that the Client connects to (by default "16444"), not for the endpoint port. Clicking it while the status shows "Allowed" removes the VisualCron firewall rule for the VisualCron Server port, which remote Clients may depend on. Open the endpoint port in Windows Firewall directly instead
- Force compression: when checked, all transfers must be compressed. The server does not offer uncompressed transfer, so connecting clients must support compression. This lowers bandwidth use but raises CPU use on the server and the client
- Use UTF8: when checked, file and folder names are exchanged with connecting SFTP clients in UTF-8. Use it when clients transfer files with non-ASCII characters in their names
- Root folder: the base folder for the endpoint files. A root folder is required
- Default Credential: the Credential used to access the root folder. It is needed when the root folder is on a network drive
- Session timeout: the session timeout in milliseconds. If "0" is entered, "360000" (6 minutes) is saved
Security options
- Allow password authentication: checked by default. Users can sign in with their password
- Allow public-key authentication: users can sign in with an SSH key pair
- Allow keyboard-interactive authentication: users can sign in with keyboard-interactive authentication
- The user must authenticate using ANY of the above methods: the default. One of the allowed methods is enough
- The user must authenticate using ALL of the above methods: every allowed method must succeed
- Private SSH key: a private key from SSH keys. The list is available only when Allow public-key authentication is checked, and the key is saved only in that case. Click the button next to the list to open SSH keys and add or edit keys
- Test key: loads the selected key and shows a check mark if the key is valid, or an error icon if it cannot be loaded
Server Settings window: FTP Endpoints tab
This tab is shown for MFT servers of type "FTP".

The grid shows the Name, IP, Security type and Port of each endpoint. The toolbar has Add, Edit, Delete and Log. Add and Edit open the FTP Endpoint window, which has the Main settings and Additional settings tabs.
FTP Endpoint: Main settings tab
-
Name: a name for the endpoint. A name is required. A new endpoint is named after its port
-
IP: the address the endpoint listens on. "0.0.0.0", the default, means all IPv4 addresses of the Server computer. The list also offers the IPv4 addresses of the computer the Client runs on
-
Security type:
- "None": the default. Plain FTP with no encryption. User names, passwords and files are sent unencrypted, and the security settings on the Additional settings tab are unavailable
- "TSL": FTPS with TLS encryption. The Client spells this value "TSL"
- "SSL": FTPS with SSL encryption
A certificate must be selected on the Additional settings tab for "TSL" and "SSL"
-
Port: the port the endpoint listens on. The default is "21". Next to the port, the window shows whether a VisualCron firewall rule exists for the port and whether another process already uses the port
-
Firewall allows: behaves as on the SFTP endpoint; see Server Settings window: SFTP Endpoints tab
-
Allow Anonymous: unchecked by default. When checked, users can connect without a user name or password
-
Use UTF8: when checked, UTF-8 is used for communication when the client supports it
-
Root folder: the base folder for the endpoint files. A root folder is required
-
Default Credential: the Credential used to access the root folder. It is needed when the root folder is on a network drive
-
Session timeout: the session timeout in milliseconds. If "0" is entered, "360000" (6 minutes) is saved
-
Outgoing speed limit: the maximum outgoing speed in bytes per second. "0", the default, means no limit
-
Incoming speed limit: the maximum incoming speed in bytes per second. "0", the default, means no limit
FTP Endpoint: Additional settings tab
The Additional security settings group is available only when the Security type is "TSL" or "SSL". The Passive mode group is available for every security type.
- Certificate with private key file (required for TLS/SSL): an X.509 certificate with a private key, selected from Certificates. It is required for "TSL" and "SSL"
- Implict SSL: when checked, the connection is encrypted from the start (implicit FTPS). When unchecked, the connection starts unencrypted and the client upgrades it (explicit FTPS). The port is not changed when this is checked
- Require TLS for control channel: when checked, clients must encrypt the command channel before they sign in. Available only for "TSL"
- Require TLS for data channel: when checked, clients must encrypt the data channel. Available only for "TSL"
With "TSL" selected and Implict SSL unchecked, unchecking Require TLS for control channel allows clients to connect without first switching the control channel to TLS, so their user name and password may be sent unencrypted.
- Use Passive mode: when checked, the server accepts passive mode (PASV) connections, where the client opens the data connection to a port on the server. This usually works better through client-side firewalls and NAT
- Passive mode host: the IP address or DNS name the server gives clients for passive connections. Available when Use Default Host is unchecked
- Use Default Host: gives clients the current IP address of the server for passive connections
- Use custom port range: limits passive connections to a port range (1 - 65535). When unchecked, random ports are used. When checked, both the start and the end of the range are required. Open the range in Windows Firewall
MFT Settings window: Users tab
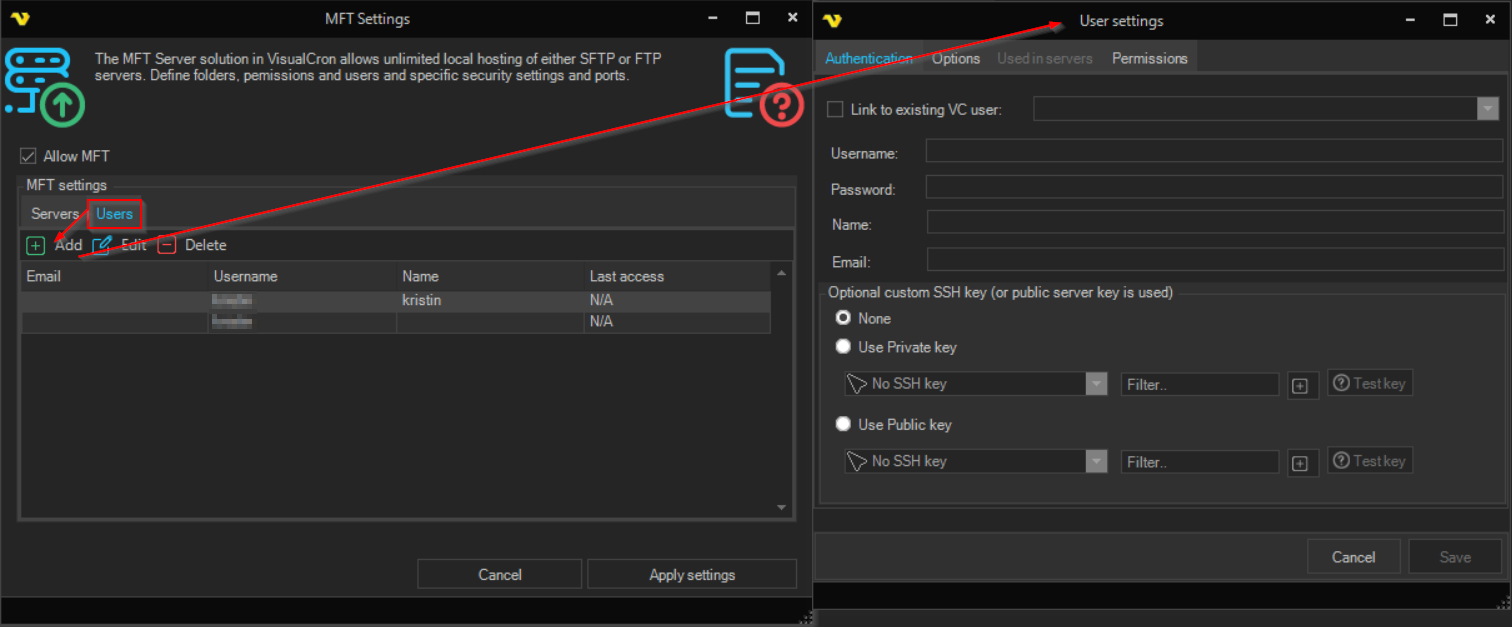
The grid lists the MFT users with their Email, Username, Name and Last access. An MFT user can be linked to an existing VisualCron user or exist only for the MFT Server. The toolbar has Add, Edit and Delete. Add and Edit open the User settings window. Delete deletes the selected users at once, without confirmation. Pressing the Delete key in the grid does the same.
Deleting a user, or deleting the VisualCron user an MFT user is linked to, removes the MFT user at once.
User settings: Authentication tab
-
Link to existing VC user: when checked, the user signs in with the user name and password of the selected VisualCron user. Username, Password, Name and Email are cleared and become unavailable. When that VisualCron user is deleted, the linked MFT user is deleted too
-
Username: the user name for an MFT-only user. A user name is required before the user can be saved and before the Used in servers tab becomes available
-
Password: the password for an MFT-only user. The password is masked
-
Name: the name of an MFT-only user
-
Email: the e-mail address of an MFT-only user
-
Optional custom SSH key (or public server key is used): the key used for this user on SFTP endpoints:
- "None": the default. No user-specific key
- "Use Private key": a private key from SSH keys
- "Use Public key": a public key from SSH keys
The key list of the selected option becomes available, and a key must be selected before the user can be saved. Use the filter field to narrow the list, the button next to the list to open SSH keys, and Test key to check the selected key
User settings: Options tab
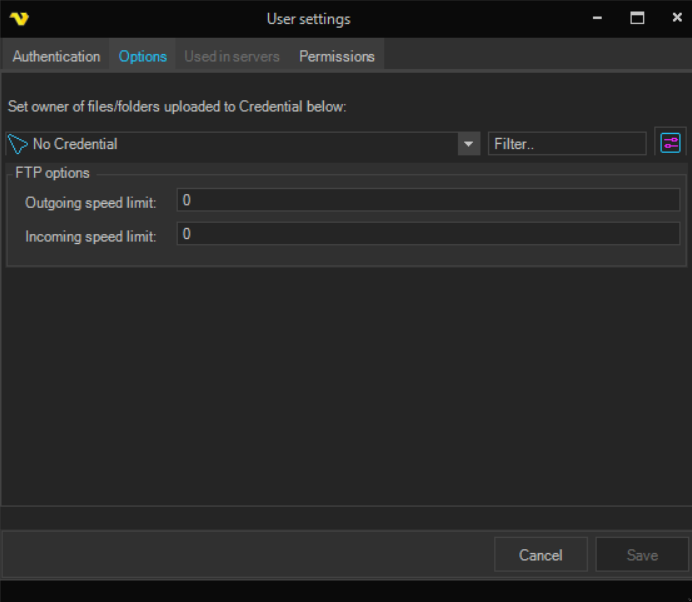
- Set owner of files/folders uploaded to Credential below: the Credential set as owner of files and folders this user uploads. Select a Credential in the combo box, or click the settings icon to open the Credential list
- Outgoing speed limit: in the FTP options group. The maximum outgoing speed in bytes per second for this user. "0" means no limit
- Incoming speed limit: in the FTP options group. The maximum incoming speed in bytes per second for this user. "0" means no limit
User settings: Used in servers tab
The grid lists the MFT servers this user has been given access to, with the server name, the server type and whether access is allowed. Add, Edit and Delete open the same Permission window as the Permissions grid on the Server settings tab.
User settings: Permissions tab
The grid lists the folder permissions of this user on one MFT server. Select the MFT server with the Server selector. Only servers the user is allowed to access are listed. The grid has the columns Folder, FR (File Read), FW (File Write), FD (File Delete), FA (File Append), DL (Directory List), DC (Directory Create), DD (Directory Delete) and DS (Directory + Subfolders).
Add and Edit open the User permissions window:
- Server: the MFT server selected in the Server selector. It cannot be changed here
- Folder: the folder on the MFT server this entry controls. Use the folder button to select a folder. A folder is required
- File Read: the user can read and download files in the folder
- File Write: the user can write and upload files to the folder
- File Delete: the user can delete files in the folder
- File Append: the user can append to existing files in the folder
- Show File List: the user can list the files in the folder
- Show Folder List: the user can list the subfolders of the folder
- Folder + Subfolders: the permissions apply to this folder and all its subfolders
- Folder Create: the user can create folders in this folder
- Folder Delete: the user can delete folders in this folder
Server Settings window: Advanced SFTP Endpoints tab
This tab is shown for MFT servers of type "SFTPAdvanced". It is the only endpoint type where the SSH algorithms can be selected.
The grid shows the Name, IP, Security type and Port of each endpoint. The toolbar has Add, Edit, Delete and Log. Add and Edit open the SFTP Endpoint window, which has the Main settings and SSH Settings tabs.
SFTP Endpoint: Main settings tab
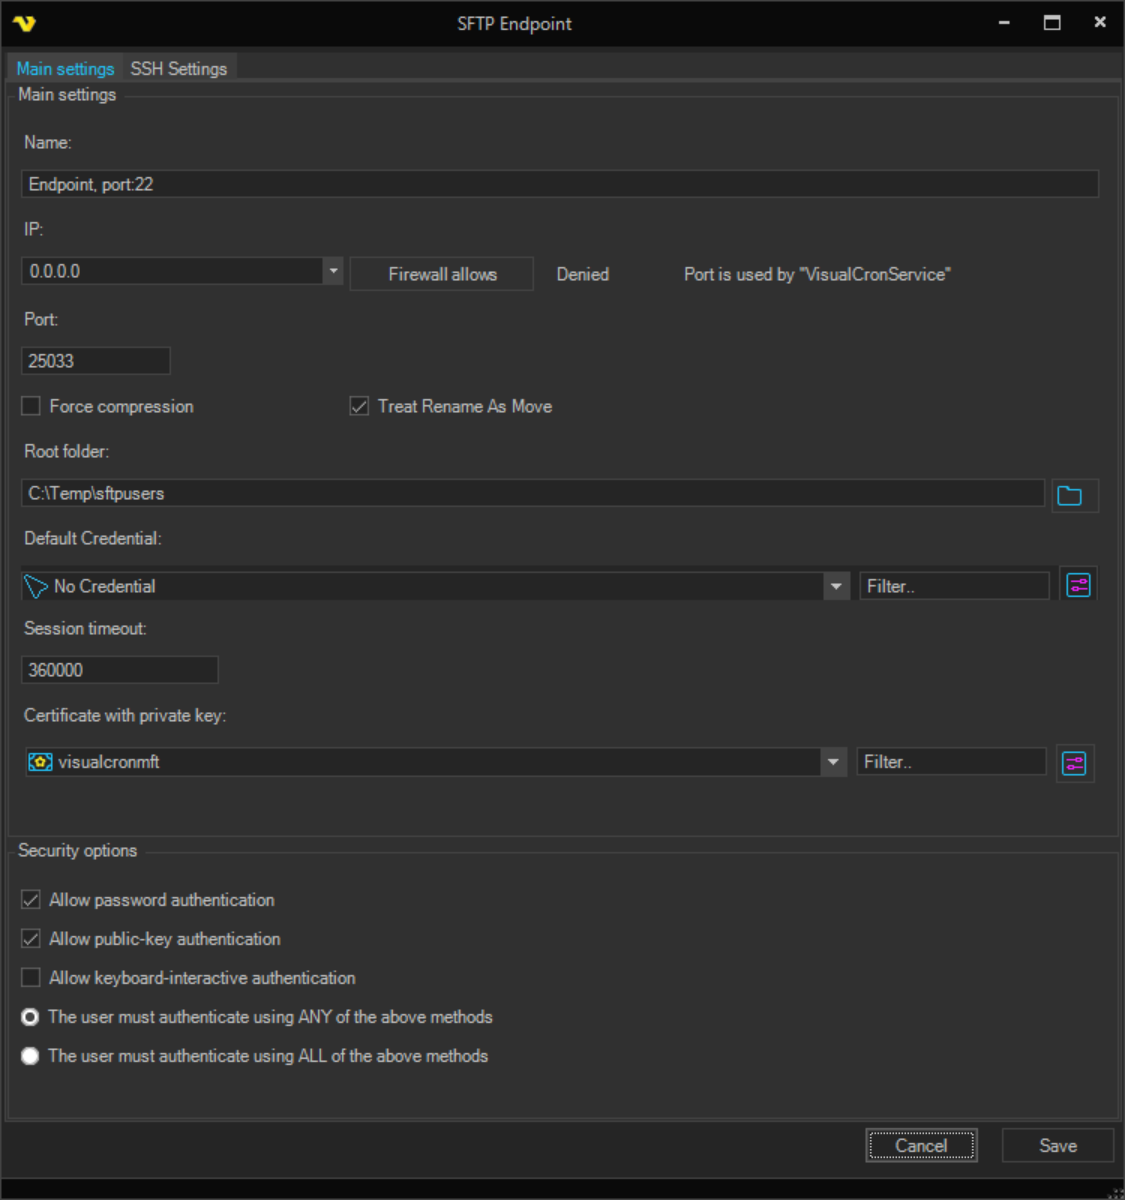
- Name: a name for the endpoint. A name is required. A new endpoint is named after its port
- IP: the address the endpoint listens on. "0.0.0.0", the default, means all IPv4 addresses of the Server computer. The list also offers the IPv4 addresses of the computer the Client runs on
- Firewall allows: behaves as on the SFTP endpoint; see Server Settings window: SFTP Endpoints tab
- Port: the port the endpoint listens on. The default is "22". A port is required
- Force compression: when checked, all transfers must be compressed. The server does not offer uncompressed transfer, so connecting clients must support compression. This lowers bandwidth use but raises CPU use on the server and the clients
- Treat Rename As Move: checked by default. SFTP rename operations are handled as move operations, which some SFTP clients need
- Root folder: the base folder for the endpoint files. A root folder is required
- Default Credential: the Credential used to access the root folder. It is needed when the root folder is on a network drive
- Session timeout: the session timeout in milliseconds. If "0" is entered, "360000" (6 minutes) is saved
- Certificate with private key: the certificate whose key the endpoint uses in the SSH connection, selected from Certificates. A certificate is required, and it must include its private key
Some older SFTP clients do not support mandatory compression. Test with the client software before checking Force compression on a production endpoint.
Security options
- Allow password authentication: checked by default. Users can sign in with their password
- Allow public-key authentication: users can sign in with an SSH key pair
- Allow keyboard-interactive authentication: users can sign in with keyboard-interactive authentication
- The user must authenticate using ANY of the above methods: the default. One of the allowed methods is enough
- The user must authenticate using ALL of the above methods: every allowed method must succeed
To require both a password and a key, check Allow password authentication and Allow public-key authentication, then select The user must authenticate using ALL of the above methods. Check that the SFTP clients support signing in with more than one method before using this setting.
SFTP Endpoint: SSH Settings tab
The Algorithms group has the Encryption algorithms, Key exchange algorithms, MAC algorithms and Public key algorithms tabs.
Each tab lists the algorithms the endpoint supports, with a Use column. Check an algorithm to offer it to connecting clients, or uncheck it to withdraw it. Select all and Deselect all below the grid set every row at once. The client and the server agree on one of the offered algorithms when the connection is made, so keep the algorithms the clients need checked.
Unchecking algorithms is how a security policy is applied to the endpoint, for example to withdraw algorithms based on MD5, SHA-1, DSA or 3DES.
A new endpoint offers several algorithms that many security policies no longer allow, including 3des-ctr, diffie-hellman-group1-sha1 and the other SHA-1 key exchanges, hmac-md5, hmac-sha1, ssh-rsa and ssh-dss. Review each list and uncheck what the clients do not need.
Encryption algorithms
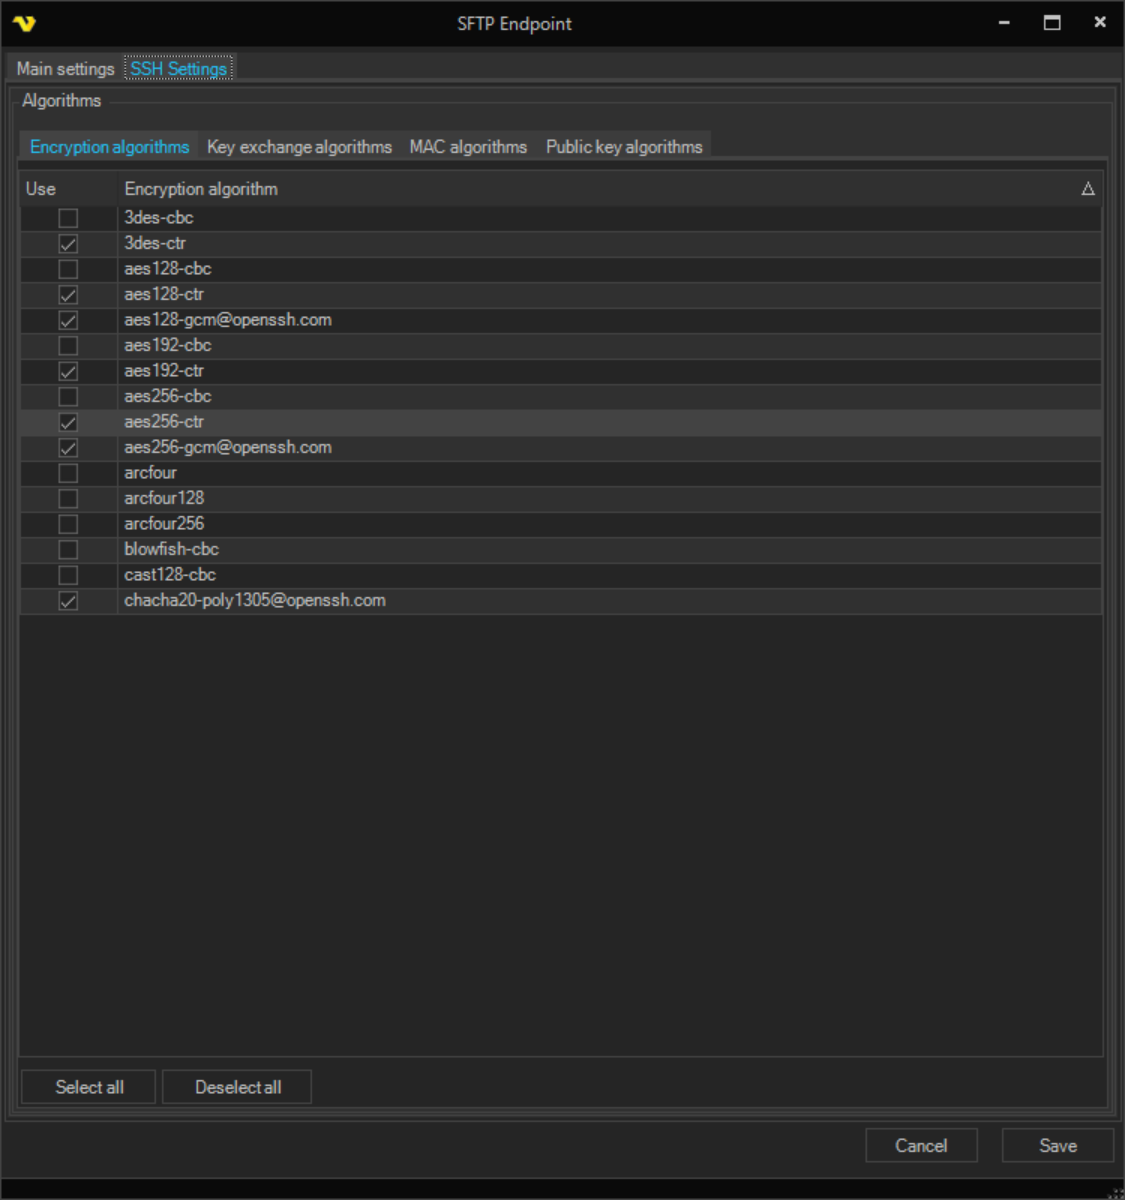
The ciphers that protect the data in an SFTP session. A new endpoint has the following checked:
aes256-ctraes192-ctraes128-ctr3des-ctraes256-gcm@openssh.comaes128-gcm@openssh.comchacha20-poly1305@openssh.com
The CBC ciphers (including 3des-cbc, blowfish-cbc and cast128-cbc) and arcfour, arcfour128 and arcfour256 are listed but unchecked.
Key exchange algorithms
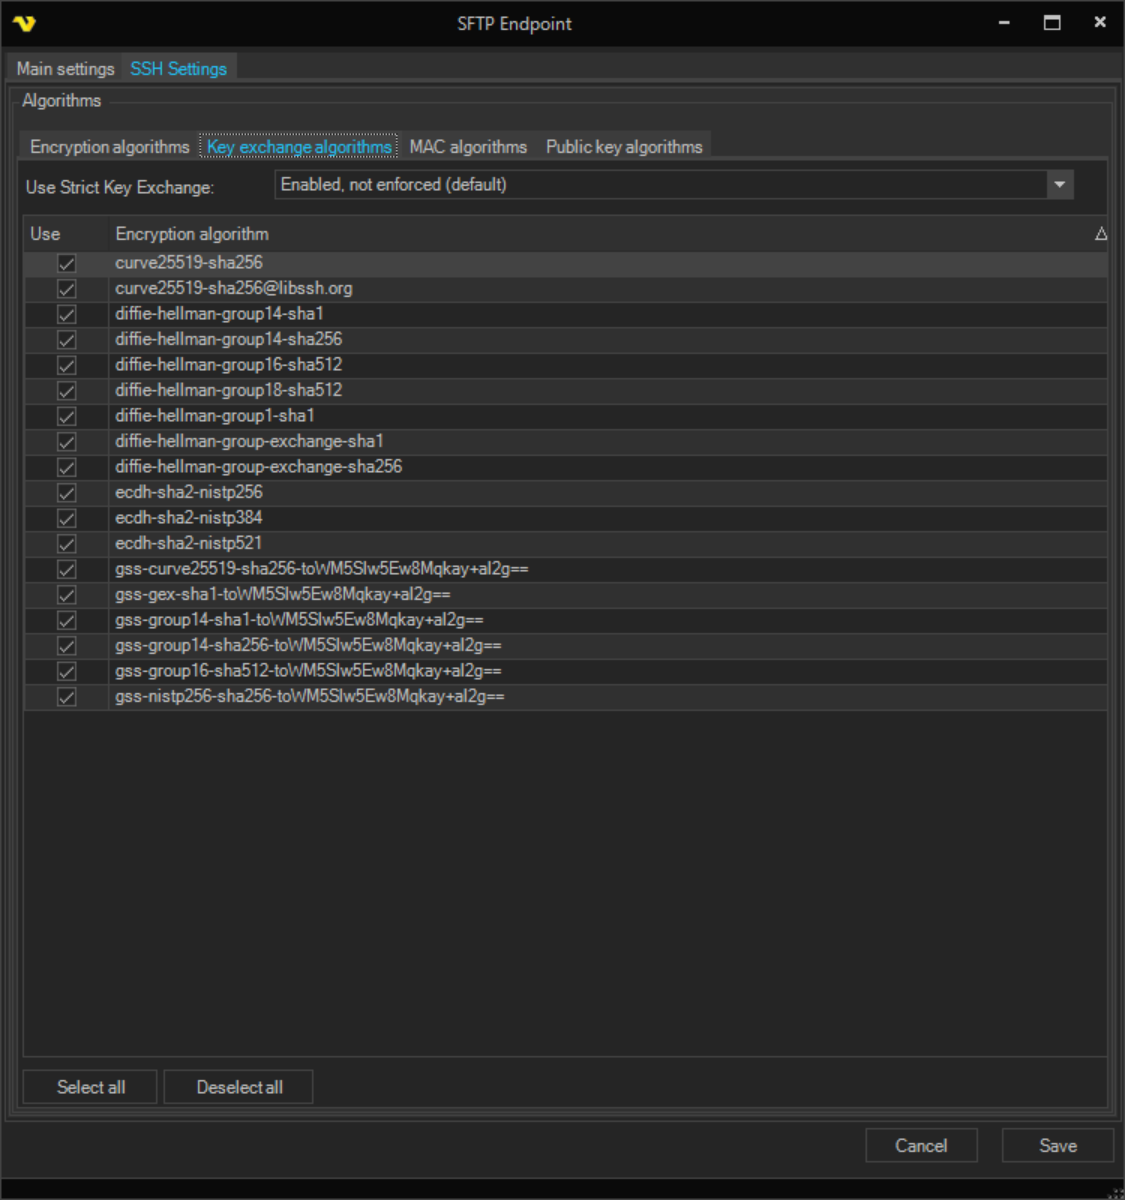
The algorithms used to agree on session keys when the connection is made, without sending the keys over the network. Every listed algorithm is checked on a new endpoint, including diffie-hellman-group1-sha1, diffie-hellman-group14-sha1, diffie-hellman-group-exchange-sha1 and the SHA-1 GSS algorithms.
- Use Strict Key Exchange: how strict key exchange is applied during the handshake:
- "Disabled": strict key exchange is off
- "Enabled, not enforced (default)": the default. Strict key exchange is on but not enforced
- "Enabled, reject affected algorithms": strict key exchange is on, and the affected algorithms are rejected
- "Required": every connection must use strict key exchange
Strict key exchange protects against some downgrade attacks, but can stop older SSH clients from connecting.
MAC algorithms
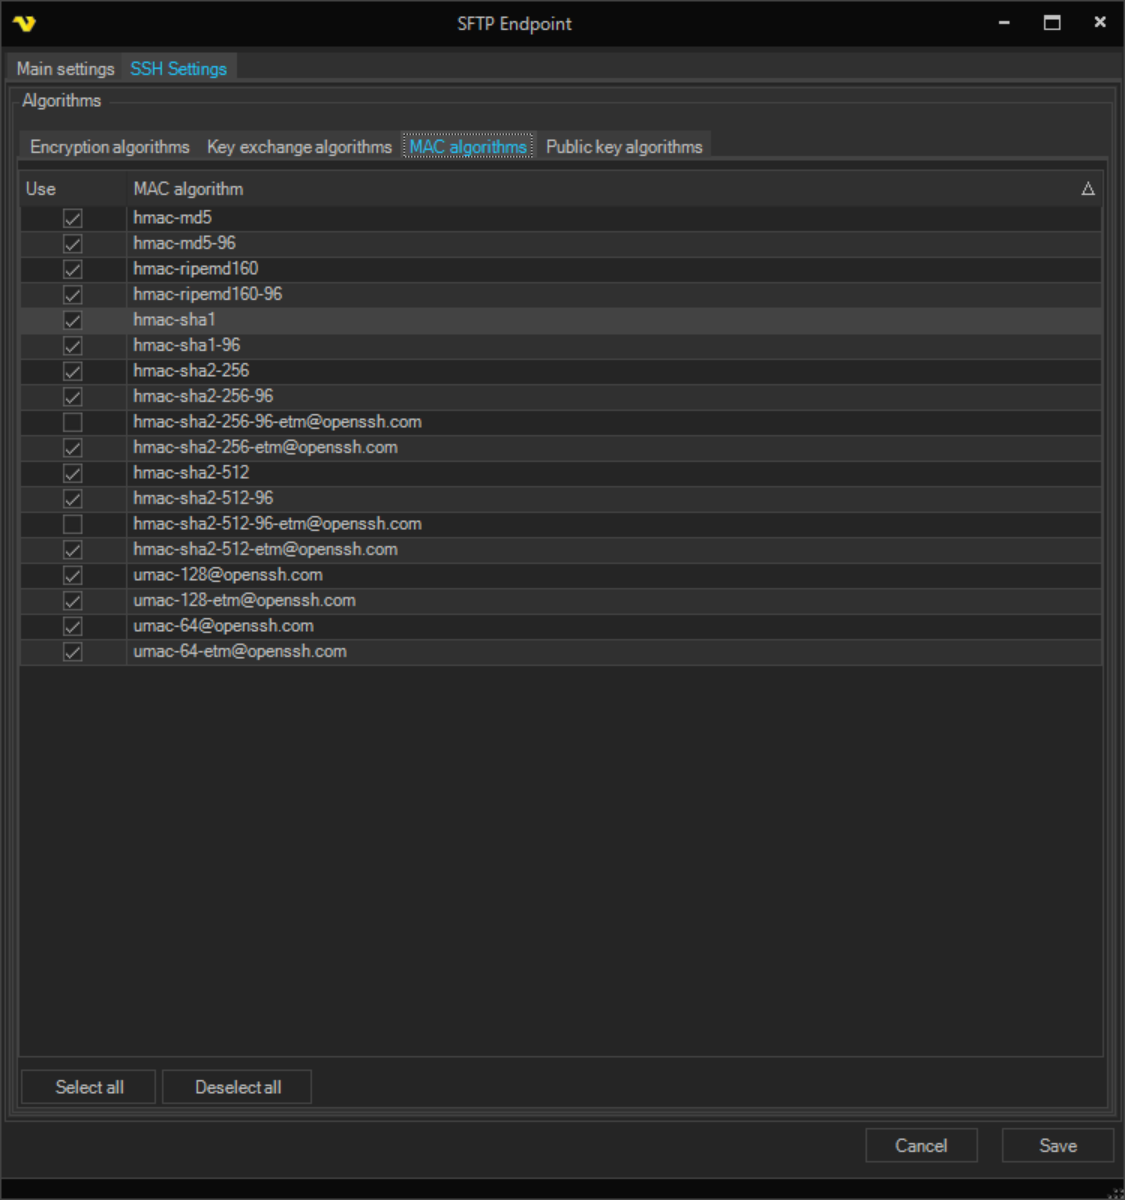
The Message Authentication Code algorithms that check that data in an SFTP session has not been changed. Every listed algorithm except hmac-sha2-256-96-etm@openssh.com and hmac-sha2-512-96-etm@openssh.com is checked on a new endpoint, including hmac-md5, hmac-md5-96, hmac-sha1 and hmac-sha1-96.
Public key algorithms
The algorithms used for the server host key and for client public-key authentication. Every listed algorithm is checked on a new endpoint, including ssh-rsa, which signs with SHA-1, and ssh-dss.
For RSA keys, both the server key and the client keys must meet the key size the organization requires. Many security standards require at least 2048-bit RSA keys.