Global - PGP Key Rings
VisualCron encrypts, decrypts and signs files with the OpenPGP standard in the PGP Encrypt and PGP Decrypt Tasks (see Task Encryption - PGP Encrypt and Task Encryption - PGP Decrypt). The keys these Tasks use are stored centrally on the Server, in key rings. This page describes the Manage PGP Key Rings window, where you create key rings, import, create, export and delete keys, and sign or revoke user IDs.
How OpenPGP uses keys
Each person or system has a key pair. The public key can be shared, and the private key stays with its owner, protected by a password.
To encrypt a file for someone, you use their public key, and only their private key can decrypt the file. The file itself is encrypted with a random session key, and only that session key is encrypted with the public key, because that is much faster.
To sign a file, you use your own private key, and others check the signature with your public key.
Key rings in VisualCron
A key ring is a named set of public and private keys, stored on the Server. Instead of pointing a Task to key files, you create or import the keys once into a key ring. In the PGP Encrypt Task, you then select the key ring, and pick the keys from it on the Recipients and Signers tabs.
To open the window, click the main menu Server -> Global objects -> PGP Key Rings. You need the PGP Key Rings permission with Read (see Permissions below).
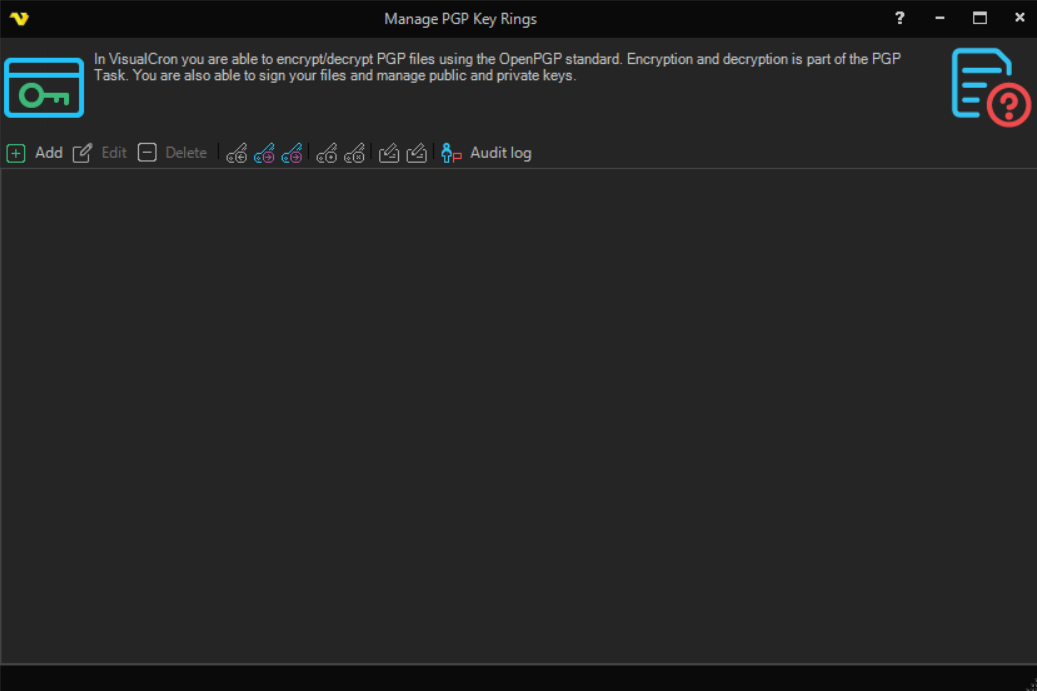
The window lists each key ring with its keys. Under each key are its user IDs and subkeys, and under those their signatures. A revoked key is marked "[Revoked]", and a subkey is shown with its algorithm and "[subkey]". A signature is shown as "Signature", or as "Revocation" when it revokes.
Delete key, and the Delete key on the keyboard when a key is selected, delete the key at once, without asking. Export the key first if you may need it again.
The Server keeps these changes in memory at first: creating, importing and deleting keys, signing and revoking user IDs, and renaming a key ring. It writes them to disk when the VisualCron service stops normally, or when a key ring is added, deleted or given a new identifier. If the Server stops unexpectedly before then, these changes are lost.
After you create or import a private key, export it with Export private key and keep the copy in a safe place.
The toolbar has these buttons:
- Add: opens the Add PGP Key Ring window (see Add a key ring)
- Edit: with a key ring selected, opens the Edit Key Ring window to rename it. Click Copy PGP Key Ring Id there to copy the key ring's identifier. To change the identifier, right-click the link and enter a new identifier in GUID format that no other key ring uses. The objects that use the key ring are updated
- Delete: deletes the key ring that contains the selection, after you confirm, even when a key inside it is selected. If other objects use the key ring, the question says how many
- Import key(s): with a key ring selected, imports a key file into it (see Import keys)
- Export public key: with a key selected, saves its public key in an ".asc" file on the computer running the Client. The proposed file name is the key's user ID, with each character that a file name can't contain replaced by "_"
- Export private key: with a key that has a private key selected, saves the private key in an ".asc" file on the computer running the Client. The proposed file name ends with "-private". For a key without a private key, VisualCron shows an error
- Create key: with a key ring selected, opens the Generate PGP key window (see Create a key)
- Delete key: deletes the selected key at once. Deleting a subkey on its own may not work. If the Server can't delete it, the subkey stays in the list, and no message is shown
- Sign selected and Revoke selected: with a user ID selected, sign or revoke it (see Sign or revoke a user ID)
- Audit log: the audit log entries for key rings
Right-click for the commands Add key ring, Edit key ring, Delete key ring, Create key, Import key, Delete key, Audit log, Versions.., Object relations, Export ... (see Import/Export - Export Settings), Send to connection ... and Send to server connection ....
Add a key ring
Click Add. In the Add PGP Key Ring window:
- Name/Description of VisualCron keyring: a name that tells this key ring apart from the others. It is required
- Under Creation options, select one of these:
- Create blank keyring (add keys later)
- Create keyring and import/paste keyring files/text (the default). Then choose one of these:
- Import from file(s) (the default): enter a Public keyring file:, a Private keyring file:, or both. The files are read by the Client, as described in Import keys. From a Client connected to a Server on another computer, use Paste key(s)
- Paste key(s): paste the key text into Public keyring: and Private keyring:
Click OK to create the key ring.
Import keys
Key files are read by the Client, on the computer it runs on. When the Client is connected to a Server on another computer, the file window shows the Server's folders. The file is then usually not found, or a file with the same path on the Client computer is read instead. Import key files from a Client running on the Server computer, or use Paste key(s) when you add a key ring.
Select a key ring and click Import key(s), then select a key file. VisualCron reads the file as a private key first, and otherwise as a public key. It then says Private key imported successfully. or Public key imported successfully., or shows an error if the file holds neither. The message appears as soon as the Client has read the file, even if the Server then refuses the key, for example because you lack Edit on PGP Key Rings. Check that the key appears in the key ring.
Create a key
The default strength of "512" bits is not secure today. Select "2048" or "4096" for new keys.
An empty password is accepted, but it leaves the private key unprotected. Always enter a password.
Select a key ring and click Create key. In the Generate PGP key window:
- Under Select encryption, select the key algorithm:
- RSA (encrypt or sign), the default: a single RSA key that can encrypt and sign
- RSA (encrypt only): an RSA signing key with a separate RSA encryption subkey
- RSA (Sign only): an RSA key for signing only
- ElGamal (encrypt only): a DSA signing key with a separate ElGamal encryption subkey
- Strength: sets the key size in bits: "512" (the default), "1024", "1536", "2048" or "4096"
- Expiry date: and Never set when the key expires. Never is checked by default, so the key does not expire. Clear Never to set an expiry date. The date starts at one year from today and can't be earlier than today
- Username: and Email: together form the key's user ID: the user name, followed by the email address in angle brackets
- Password: and Repeat password: set the password that protects the private key. The two must match
Elliptic curve (ECC) keys are not offered.
Click OK. The key is generated on the computer running the Client, which can take a while for large keys, and is then added to the key ring on the Server. If generation fails, VisualCron shows the error and adds nothing. If the Server refuses the key, for example because you lack Edit on PGP Key Rings, no message is shown. Check that the key appears in the key ring.
The encryption algorithm for your files is selected separately in the PGP Encrypt Task, where AES-256 is available (see Task Encryption - PGP Encrypt).
If you need a key with specific protection or preference settings, create it in a dedicated PGP tool, such as GnuPG or Kleopatra. Then import it into a VisualCron key ring with Import key(s).
Sign or revoke a user ID
Select a user ID under a key, and click Sign selected or Revoke selected. In the Select key window, select the private key to sign or revoke with in Private key:, enter its password in Password:, and click OK. The Server signs or revokes the user ID and updates the key ring.
Permissions
Key rings are governed by the PGP Key Rings permission (see Main - User Permissions and Supported Permissions):
- Read: open the Manage PGP Key Rings window and see the key rings, and also Export private key
- Add: add a key ring with Add. Import key(s) and Create key need both Add and Edit. Without Edit, the Server adds nothing, but after Import key(s) the Client still reports success
- Edit: Edit, Sign selected and Revoke selected
- Delete: Delete, in the Client. Delete key needs Delete and Edit. Without Edit, the key stays, and no message is shown
The file windows for import and export also need the Remote file explorer permission with Read.
Read alone lets a user export a key together with its private key. The built-in Viewers group has Read on PGP Key Rings. Clear it in the Viewers group, and give Read on PGP Key Rings only to users you trust with the private keys.
The Server doesn't check Delete when a whole key ring is deleted. Only the Client checks it. Any logged-on user can therefore delete a key ring through the VisualCron API, whatever their Delete permission. Give logons to the Server only to trusted users, and export the key rings you can't afford to lose.